Rewriting these files may have led to an automatic logout from the user’s account, however not more than that. It is crucial to store passwords in a means that forestalls them from being obtained by an attacker even when the appliance or database is compromised. Most modern languages and frameworks provide built-in functionality to help retailer passwords safely. In a 2017 research (updated in 2021), cybersecurity agency Venafi polled over 430 IT professionals answerable for the cryptographic belongings of their company’s DevOps applications. The research revealed that many organizations fail to enforce important certificates security measures of their DevOps environments.
One of the most important steps DevOps groups can take is protecting their cryptographic property. DevOps teams use cryptographic keys and certificates to protect information in transit and at relaxation, both during improvement and of their final merchandise. As technology and threats evolve, so should your analytical skills and curiosity.
Defending Data At Rest
Prioritization should account for operational dependencies, compliance obligations, and the effort required for migration. Symmetric encryption transforms readable plaintext into ciphertext that’s unintelligible with out the proper decryption key. This protects data each in transit (when transferring across networks) and at rest (when saved in databases, disks, or cloud environments). Even if an attacker intercepts encrypted data, they can’t read it without the vital thing.
The relationship between the builders who implement cryptographic algorithms and the top customers whose information these algorithms shield isn’t direct. Multiple layers of supply chain relationships separate the 2, and cryptographic weaknesses in system parts may be hidden from the enterprise that ultimately bears the risk. A vendor may use an outdated library, a supplier could misconfigure an algorithm, and the organization counting on the ultimate product has no visibility into the underlying cryptographic implementation.
Three Employing Stateful Hash-based Signature Schemes
Make The Most Of our cloud-hosted platform or your individual learning management system to get recent and related content material authored, up to date, and launched by solely high experts in the application security group. There are lots of good sources of cryptography training out there, together with the OWASP cheat sheets we’ve linked to here. Black Duck additionally provides an array of coaching alternatives, together with our eLearning merchandise.
Equally to the factoring problem, it builds a trapdoor, i.e., a function that’s simple to compute using the general public key however is hard to invert with out knowing the personal key. Cryptography is taken into account as a department of each arithmetic and computer science, and it is related carefully to data safety. This chapter explores the earliest known cryptographic strategies, together with the scytale, Caesar cipher, substitution ciphers, and transposition ciphers. The development of symmetric and asymmetric key cryptography, hash capabilities, and digital signatures is also mentioned. The chapter highlights major historical events and technological advancements which have pushed the need for stronger and more efficient encryption strategies.
What’s Cryptography? The Way To Defend Data Within The Digital Age
Quantum computers are computers that harness phenomena from quantum mechanics, corresponding to superposition and entanglement, to perform operations that classical computers can not carry out. Current small quantum computer systems have been developed, notably the IBM Q System One, but they’re nonetheless outperformed by classical computer systems at present. Cryptography thus complements policies that management data access and execution. The protocol events exchange greater than Q qubits, and since storage is restricted, a large a part of the transferred knowledge must either be measured or discarded. Forcing dishonest parties to measure a large part of the data permits the protocol to avoid the impossibility end result. When each events want reassurance that the other side is participating with good intention, then mistrustful quantum cryptography is a wonderful answer.
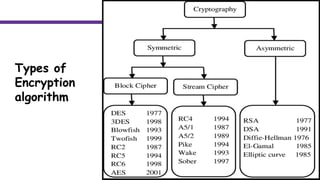
Widely utilized in many cryptographic protocols similar to Safe Socket Layer (SSL)/Transport Layer Safety (TLS), Secure Shell Protocol (SSH), and Virtual private networks (VPNs) 31, 32. However, it does not provide authentication 32, and therefore a man-in-the-middle assault is possible if the channel isn’t https://bonnefication.com/auto-fabrica-type-5-triumph/ authenticated. To tackle this issue, DH is usually used in combination with digital signatures or different authentication mechanisms 33. Symmetric key cryptography is among the oldest and most widely used types of encryption. It relies on the idea of using the same key to encrypt and decrypt a message.
- Equally to the factoring problem, it builds a trapdoor, i.e., a function that’s simple to compute utilizing the basic public key however is tough to invert with out figuring out the personal key.
- Moreover, cryptography underpins safe backups and integrity verification.
- On the contrary, stream ciphers, together with Rivest Cipher four (RC4), encrypt information in either one bit or a byte at a time.
- Symmetric and asymmetric encryption solve totally different problems, so the best comparability just isn’t “which is better” however “which matches this job.” The desk beneath summarizes the commerce offs that matter most for a variety determination.
- This chapter provides an summary of varied cryptographic techniques, together with symmetric and asymmetric encryption, hashing, digital signatures, homomorphic encryption, multiparty computation, and lightweight cryptography.
Digital signatures can be utilized in a variety of functions, together with software program updates, on-line transactions, and legal documents. They present a means of verifying the id of the sender, making certain the integrity of the message or doc, and stopping the sender from denying that they despatched the message or document. Diffie-Hellman (DH) is a key exchange algorithm that enables two events to ascertain a shared secret key over an insecure channel. It was developed by Whitfield Diffie and Martin Hellman in 1976 and relies on the discrete logarithm problem in modular arithmetic. Producing actually random keys which are so long as the plaintext is a difficult task, and transmitting them securely to the recipient is also a difficult problem.
Cryptographic secrecy goes even additional, requiring that not one bit of information ought to be uncovered about the plaintext from the ciphertext without figuring out the necessary thing. This is called Kerckhoffs’s principle, which states that the security of an encryption algorithm resides in the secrecy of the encryption key. The whole encryption algorithm can therefore be public, and the security guarantees nonetheless maintain as lengthy as the secrecy of the encryption secret is maintained. The three main sorts are symmetric encryption (one shared key for both encryption and decryption), uneven encryption (a public/private key pair), and hash functions (one-way transformations used to verify data integrity).